………………………………….
Published in association with
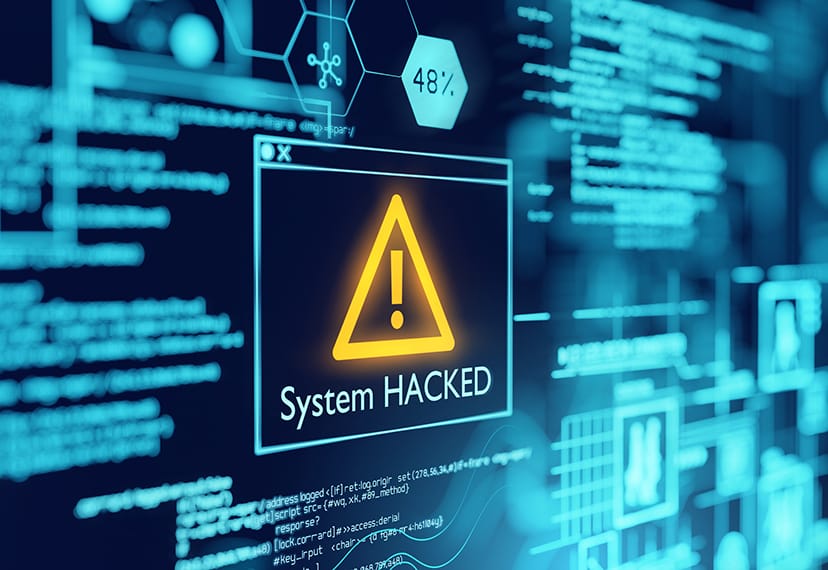
THE HEAD of a Kettering-based logistics company that was forced into administration following a major ransomware attack has stressed the importance of having robust cybersecurity measures in place – not simply relying on off-the-shelf solutions.
In June 2023, KNP Logistics Group suffered a major ransomware attack, which affected key systems, processes and financial information.
It is thought the attackers were able to access the company’s systems by exploiting a weak password used by a member of staff, using software to ‘brute force’ attack (meaning many different combinations were tried until the correct one was found).
Crucially, the company had not enabled multi-factor authentication.
Despite having taken out cybersecurity insurance three weeks before and having complied with requirements for an international data security accreditation, that did not prevent the company from going under.
Faced with challenging market conditions and unable to secure urgent investment due to the attack, the business went into administration, with around 730 employees made redundant.
What is ransomware?
Ransomware is a type of malicious software (malware) designed to block access to a computer system or data until a ransom is paid. It typically encrypts the victim’s files, making them inaccessible, and demands payment (usually in the form of cryptocurrency) for the decryption key needed to unlock them.
Victims of ransomware are increasingly facing an extortion threat too, with cybercriminals also threatening to publish or sell stolen data unless a ransom is paid.
It is generally spread through phishing emails, malicious websites or by exploiting vulnerabilities in software.
How do ransomware attacks work?
Systems are accessed. Typically when a user inadvertently downloads something that will execute the ransomware.
Files are encrypted. Once the malware has been executed, it will encrypt files on the infected system, making them inaccessible.
Demands are made. A ransom note will then be displayed, making demands in exchange for the decryption key needed to access the files.
Decryption. If the ransom is paid, the attackers may then provide the decryption key needed. However, there is no guarantee of that.
Should businesses pay the ransom?
It is believed that ransomware victims paid approximately $460 million to ransomware groups in the first half of 2024 alone – a 2% increase from the previous year’s record-breaking ransom payments.
The National Cyber Security Centre and insurance industry bodies the Association of British Insurers, the British Insurance Brokers Association and the International Underwriting Association recommend that victim organisations review the following guidance before paying a ransom to a criminal group. Visit https://www.ncsc.gov.uk/guidance/organisations-considering-payment-in-ransomware-incidents
The impact of ransomware attacks
As seen with the experiences of KNP Logistics Group, ransomware attacks can have severe consequences – or even be fatal – for businesses, including causing:
- Business disruption.
- Financial loss.
- Reputational damage.
- Legal and regulatory consequences.
Protecting your business from ransomware
There are a number of steps that businesses can take to safeguard themselves against ransomware attacks.
Employee training Educate your employees about the dangers of phishing emails and the importance of not clicking on suspicious links or attachments.
Regular backups Regularly back up critical data and store backups offline or in a secure cloud environment. This ensures that you can restore your data without paying the ransom.
Security software Ensure you have reputable antivirus and anti-malware software in place to help detect and block cyber threats.
Patch management Keep all software and systems up to date with the latest security patches to prevent attackers from exploiting known vulnerabilities.
Access controls Implement strict access controls to limit the spread of ransomware within your network. Use multi-factor authentication (MFA) to secure sensitive accounts.
Incident response plan Develop and regularly update an incident response plan to quickly and effectively respond to ransomware attacks.
The successful cyberattack on KNP Logistics Group serves as a poignant reminder of the devastating impact ransomware attacks can have for businesses.
While off-the-shelf cybersecurity solutions may seem like an easy option, they can struggle to keep up with sophisticated and evolving threats. We would therefore always recommend speaking to a specialist company, such as ourselves here at Dragon IS, to ensure your cybersecurity is as robust as it needs to be.
Alongside this, businesses need to be investing in employee training and awareness and should have a comprehensive incident response plan in place, to help limit any disruption and protect their operations.
In need of expert support?
Dragon IS works with small and medium-sized businesses, helping them with a broad range of issues relating to their IT infrastructure and cybersecurity. To find out more email [email protected] or call 0330 363 005.
………………………………….
Stay connected with local business through Business MK. Join our exclusive community for the latest news, insights, updates, features and thought leadership.
Stay informed – subscribe now at bit.ly/3MZiqzQ. Unsubscribe at any time.